






Binance founder Changpeng Zhao (CZ) shared a security playbook after four data leaks hit two major crypto exchanges and two Korean finance firms on the same day. Each crypto data leak, he warned, feeds phishing, SIM swaps, and social engineering.
Funds stayed safe in every case reported so far. However, leaked names, emails, and phone numbers hand scammers a ready list of exchange users with balances worth targeting.
Sponsored
Sponsored
How CZ Wants Users to Stay SAFU After a Crypto Data Leak
4 data leaks reported today:
1. Coinbase's vendor Amplitude exposed some users contact data (funds unaffected).
2. Bithumb (Korea) had user data leaks.
In TradFi, two securities firms in Korea leaked data:
3. Mirae Asset
4. Daishin Securities
You can't prevent a leak, but…
— CZ ???? BNB (@cz_binance) October 28, 2026
SAFU began as a 2018 crypto meme that misspelled “safe.” Binance later named its emergency reserve, the Secure Asset Fund for Users, after it.
First, Zhao urged users to set up a unique email alias for every exchange. A leak then stays isolated, and users can see which service lost their data.
The Binance founder also advised against SMS-based two-factor authentication (2FA). Instead, he recommended hardware keys, passkeys, or authenticator apps, since leaked phone numbers are the main route to SIM swaps.
In addition, anyone who reaches out about security issues or refunds should count as a scammer, Zhao said, even if they know account details. Recent Passport wallet phishing emails, for example, contained recipients real home addresses.
Sponsored
Sponsored
When one user replied that phishing emails kept arriving, Zhao told them to change the address quickly.
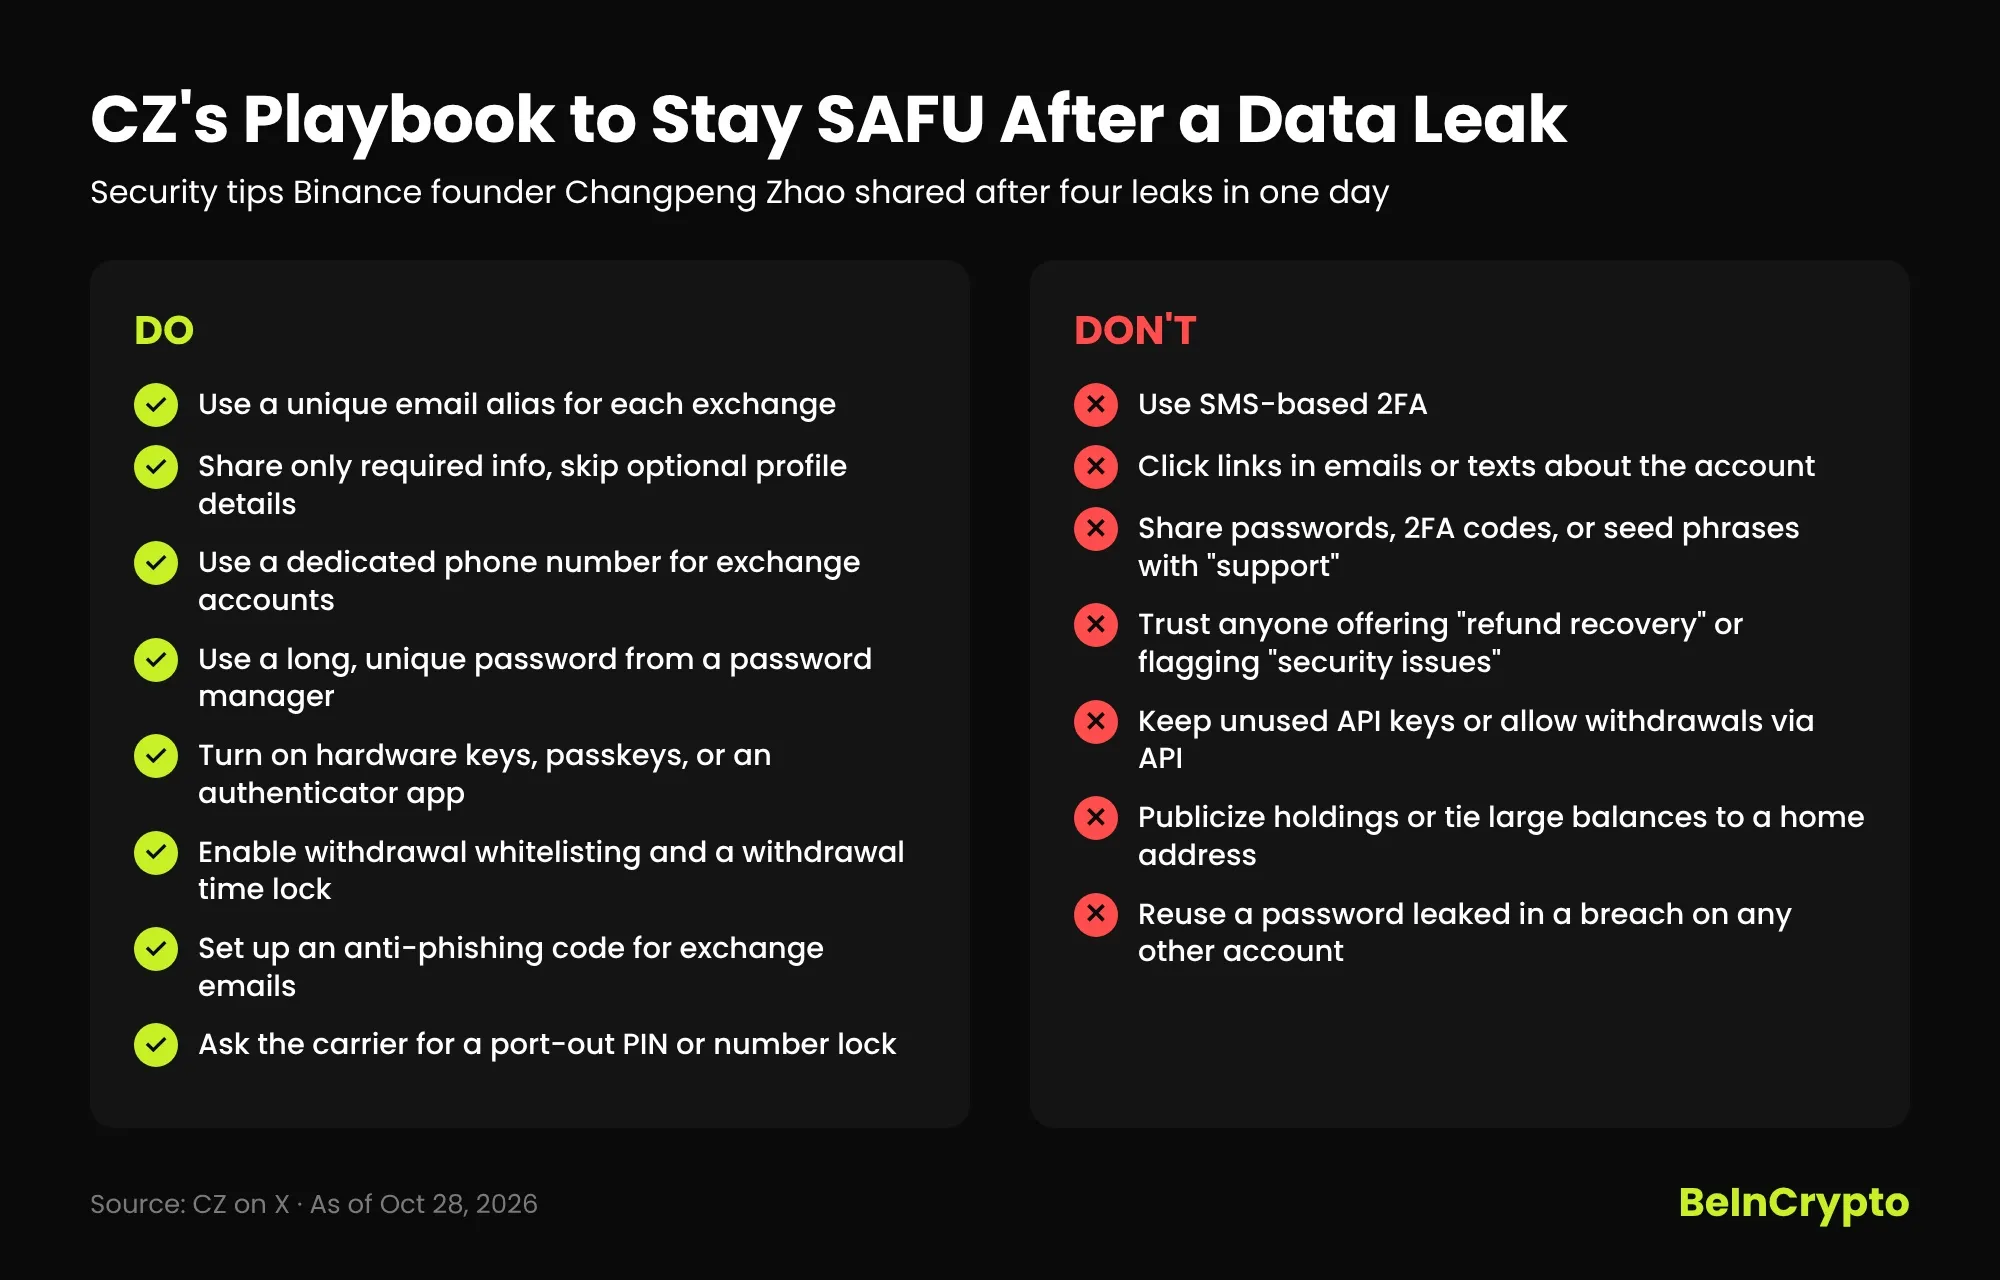
CZs Playbook to Stay SAFU After a Data Leak. Source: BeInCryptoWhy the Latest Leaks Raise the Stakes
At Coinbase, the exposure came through Amplitude, a US analytics vendor, according to Zhao. Meanwhile, Bithumb found on October 27 that an outsider had entered its internal mobile groupware system, the Korea Times reports.
In traditional finance, Daishin Securities confirmed a leak affecting 38,490 customers. By contrast, Mirae Asset Global Investments says hackers saw only some employee names.
Bithumbs case adds a crypto data leak to a wave of attacks on Korean finance that began at Shinhan Bank in late September. The suspected attacker behind earlier Korean bank breaches reportedly asked an AI tool where to sell stolen data.
Physical risk is growing as well. Leaked addresses combined with holdings data have enabled so-called wrench attacks, which netted criminals an estimated $30 million in thefts in the first half of 2026.
Last week, Zhao argued that leaked data fuels phishing more than any AI attack on Bitcoins cryptography. Within days, four new leaks handed scammers fresh contact data across both crypto and traditional finance.