




The hard fork on Monday followed a majority of Gnosis validators adopting a soft fork in response to a November Balancer exploit, in which about $116 million in crypto was stolen.
Gnosis chain operators executed a hard fork to recover funds tied to a $116 million Balancer exploit in November.
In a Tuesday X post following a notice for node operators, Gnosis said it executed a hard fork to recover some of the funds from a significant exploit of Balancer. The project said the funds were “out of the hacker's control,” signaling a partial or full recovery.
The hard fork, executed on Monday, followed a majority of validators adopting a soft fork in November in response to the Balancer exploit affecting “Balancer‑managed contracts on Gnosis Chain.”
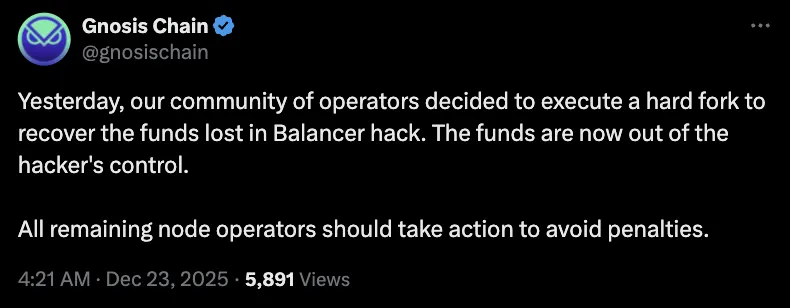
Source: Gnosis Chain
“There is still a live community discussion around how people will be able to claim back their funds, as well as how contributors involved in the rescue mission may be recognized or compensated,” said Gnosis head of infrastructure Philippe Schommers in a Dec. 12 forum post. “Right now were focused on enabling funds to be recovered by Christmas. Once they sit safely in a DAO controlled wallet we will figure out everything else.”
On Nov. 3, Balancer reported that the decentralized exchange and automated market maker had been exploited for more than $116 million worth of digital assets. Onchain data showed a hacker transferred millions in staked Ether (ETH) to a new wallet.
Related: Balancer exploit swells to $116M in outflows as team offers 20% bounty
Though Balancer later reported that white hat hackers had managed to recover about $28 million of the stolen funds, it did not appear to have regained access to the majority of digital assets.
11 audits didnt prevent the Balancer exploit
According to a list of Balancer V2 audits available on GitHub, four different security companies conducted 11 audits of the platforms smart contracts. The project reported that the exploit was “isolated to V2 Composable Stable Pools.”