Event Details
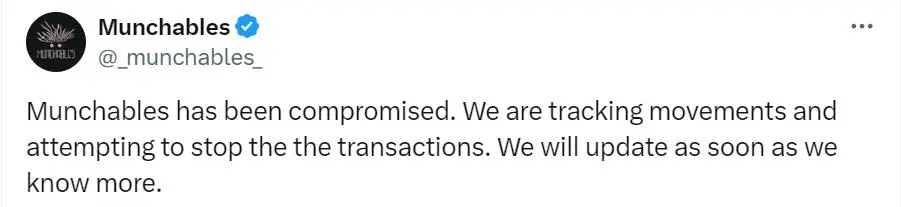
Blast ecosystem project Munchables has announced on the X platform that it has been attacked. The project is currently tracing the flow of funds, attempting to halt transactions, and will update relevant information as soon as possible.
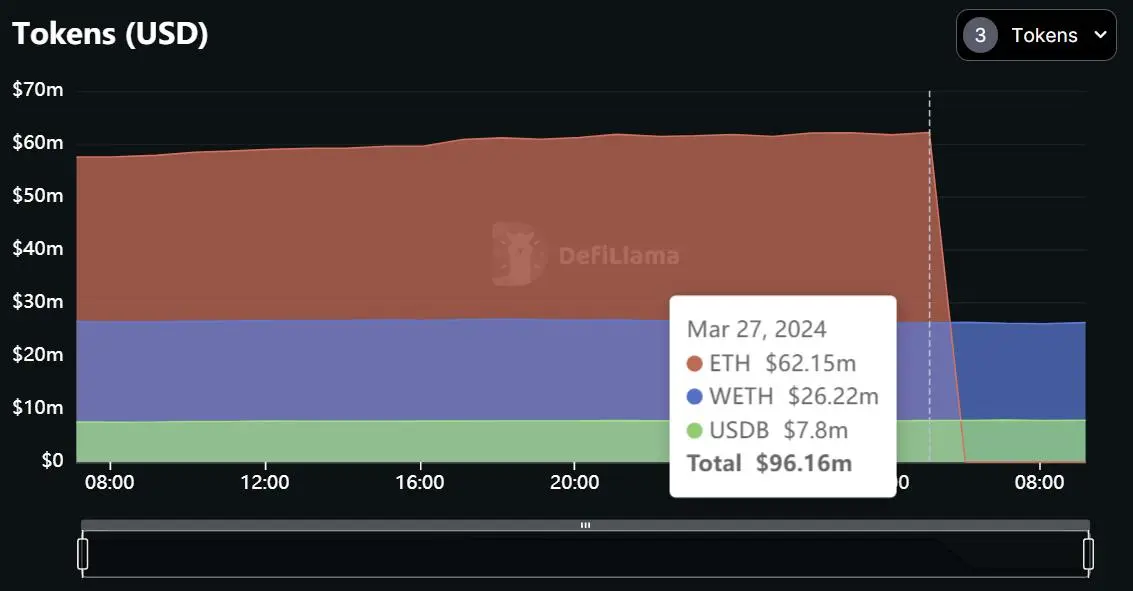
According to data from Defillama, Munchables had a Total Value Locked (TVL) of $96.16 million before the theft. In this hacking incident, all the ETH in the protocol was stolen, resulting in a loss of over 17.4K ETH, which is approximately $62.5 million at the current price.
Slowmist founder Cos commented on the Munchables attack on Blast, stating, “The Munchables protocol on Blast was stolen $62.5 million, a significant loss. According to the investigation by on-chain detective ZachXBT, it was because one of their developers is a North Korean hacker... This is at least the second DeFi project we have encountered with such a situation. The core developer disguised themselves and lurked for a long time, gaining the trust of the entire team. Once the time was right, they struck without mercy. There are likely many victims, and we will closely follow up.”
On-chain analyst @SomaXBT posted that the Blast ecosystem project Munchables, which was hacked, had previously hired an unknown security team @EntersoftTeam to produce an audit report in order to save on audit fees. The team's account description claims, “We are an award-winning application security company with certified ethical hackers.”
Additional Information Compilation
Juice Finance: In the Blast ecosystem, DeFi protocol Juice Finance has stated that all wETH of Juice users are still within the Munchables contract. Currently, approximately 7,277 ETH (worth $26.25 million) is temporarily frozen in the Munchables contract. Juice Finance will do its utmost to assist Munchable in recovering the funds.
AAVE Gotchi Founder CoderDan: The development team of Aavegotchi, Pixelcraft Studios, had briefly employed the Munchables attacker for some game development work. His technical skills were rough, and he genuinely felt like a North Korean hacker. We fired him within a month. At that time, Pixelcraft Studios had some video calls with him, but no recordings were made. Additionally, CoderDan provided the Munchables team with the usual addresses of the hacker when he was employed at Pixelcraft Studios.
SlowMist: Between the two addresses related to the Munchables hacker, not only are there transactions but also interactions with multiple exchanges, most commonly with Binance, MEXC, and ChangeNOW.
ZachXBT: It appears that the four developers hired by the Munchables team might be the same person.