




Revolut said Thursday it had received no direct contact from those claiming responsibility for a customer data breach despite multiple public ransom demands.
A group calling itself “IAmNotAVillain” publicly demanded 6,000 Monero (XMR), worth about $3 million, from Revolut within 24 hours, threatening to sell the customer records to other criminal groups, the Financial Times reported Wednesday.
“Revolut has not received any direct contact or demand from the individuals or group making these claims,” a Revolut spokesperson told Cointelegraph.
The public ultimatum is the latest development in a data breach Revolut first disclosed last week, with Italian authorities now widening their investigation into how a government email account was allegedly used to obtain customer data.
One breach, multiple ransom demands
Revoluts claim that it has received no direct contact adds to uncertainty over who is behind the public ransom demand, as “IAmNotAVillain” is not the only name linked to claims of responsibility for the incident. Its website, iamnotavillain.xyz, was unavailable when checked by Cointelegraph at the time of publication.
An earlier group calling itself “Revolut Smilik” reportedly demanded 10,000 Bitcoin, worth about $780 million at the time, vastly more than IAmNotAVillains current $3 million Monero demand.
IAmNotAVillain disputed the competing claim in a notice on its website, alleging that a former associate had received only a small sample of the data before taking credit for the breach. The site warned others not to deal with the rival claimant.
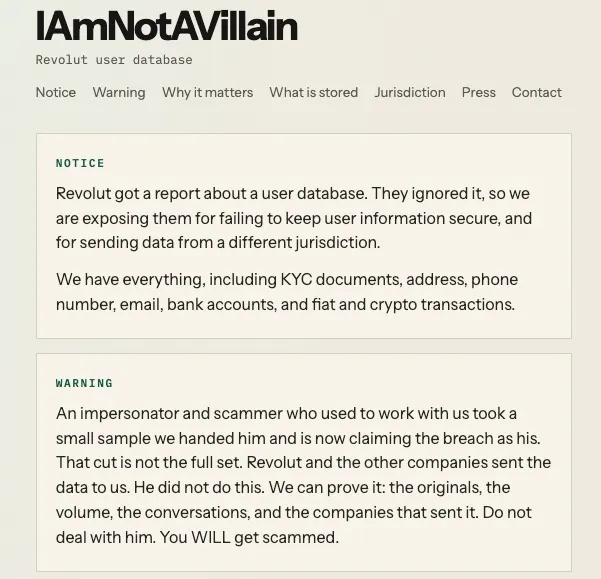
An archived version of the IAmNotAVillain website. Source: Internet Archive
Cybersecurity-focused account Dark Web Informer also flagged another website, revoloot.lol, associated with a separate actor claiming responsibility, further complicating efforts to establish who controls the stolen customer records. The revoloot.lol website was also unavailable when checked by Cointelegraph.
Italian authorities widen Revolut data breach probe
Italys National Anti-Mafia and Anti-Terrorism Directorate is also now involved because the suspected intrusion concerns a government entity, Italian news agency ANSA reported Wednesday.
Related: Italy investigates government email breach linked to Revolut data leak
Prosecutors in Reggio Calabria have opened an investigation into unauthorized access to a computer system of public interest, while investigators work to establish whether the institutional email account was breached or cloned.
Italys privacy regulator has separately asked banks to urgently review the security of their access systems and is examining whether other banks or financial institutions may have been involved.