




One of the most successful MEV bots in crypto, Jaredfromsubway.eth, has been drained for more than $7.5 million, with an attacker exploiting the bots automated systems, the same ones that have netted it hundreds of millions over the years.
According to Blockaid, the incident on Saturday resulted from attacker-controlled contracts tricking Jaredfromsubway.eths automated MEV execution system into granting token approvals that were later used to drain funds.
“This is not a classic phishing attack and not a traditional smart-contract vulnerability in the victim contract,” Blockaid said on X.
Its a rare comeuppance for MEV (maximal extractable value) bots like Jaredfromsubway.eth, which are automated programs that monitor unconfirmed transactions on blockchain networks and manipulate their order to extract profit, a kind of “invisible tax” on DeFi users.
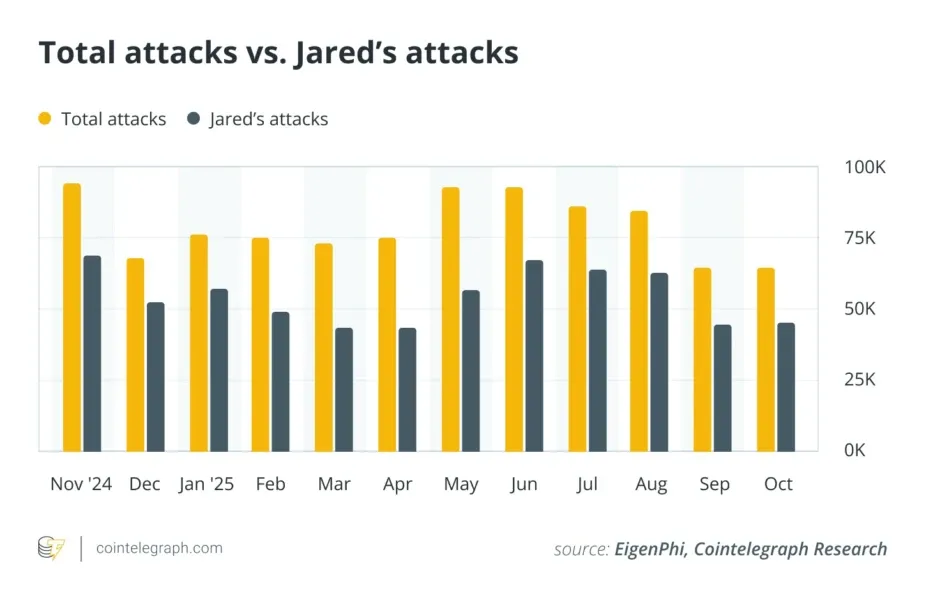
Cointelegraph Research previously found that sandwich attacks on Ethereum have resulted in about $60 million in annual losses for traders. The research also found that between November 2024 and October 2025, there were 60,000 to 90,000 sandwich attacks per month, with roughly 70% of them associated with Jaredfromsubway.eth.
How Jaredfromsubway.eth was exploited
The attacker created fake wrapper tokens and pools, including fake Wrapped Ether (fWETH), fake $USDC (fUSDC) and fake USDt (fUSDT) routes paired with fake Cap (fCAP), Blockaid explained.
The fakes were designed to look like profitable trades, the kind the MEV bot is programmed to chase. It then did what it was designed to do, approving certain attacker-controlled helper contracts to spend real money on its behalf.
While in normal cases, the bot would use up the approval during the trade, in this case, the attacker crafted routes that allowed the approvals to stay open.
Once enough approvals were in place, the attacker conducted a “final sweep” to pull WETH, $USDC and USDT from the Jaredfromsubway.eth MEV bot contract via transferFrom.
“The attacker exploited the bots mechanism: its automated system detected what looked like profitable MEV opportunities and generated approvals to attacker-controlled helper contracts.”
“We shouldn‘t be happy about this; no one should celebrate ... but if you’ve ever been sandwiched by this ... I‘m pretty sure you’re not upset about this news,” crypto investor and commentator David Gokhshtein said.