




Every step of that runs on the attacker's machine. The victim's device is not involved at any point and could be powered off in a safe on another continent.
Galaxy's breakdown shows the process running. Of the drained wallets, 1,183 used the modern native segwit address format, seven used an older standard and six an older one still. Nobody targets a specific victim across three address formats at once.
That is systematic enumeration, checking each candidate seed against every path it might have produced. The operator can widen the search, refine it and return whenever they choose.
Galaxy warned further waves are likely if owners do not move their funds.
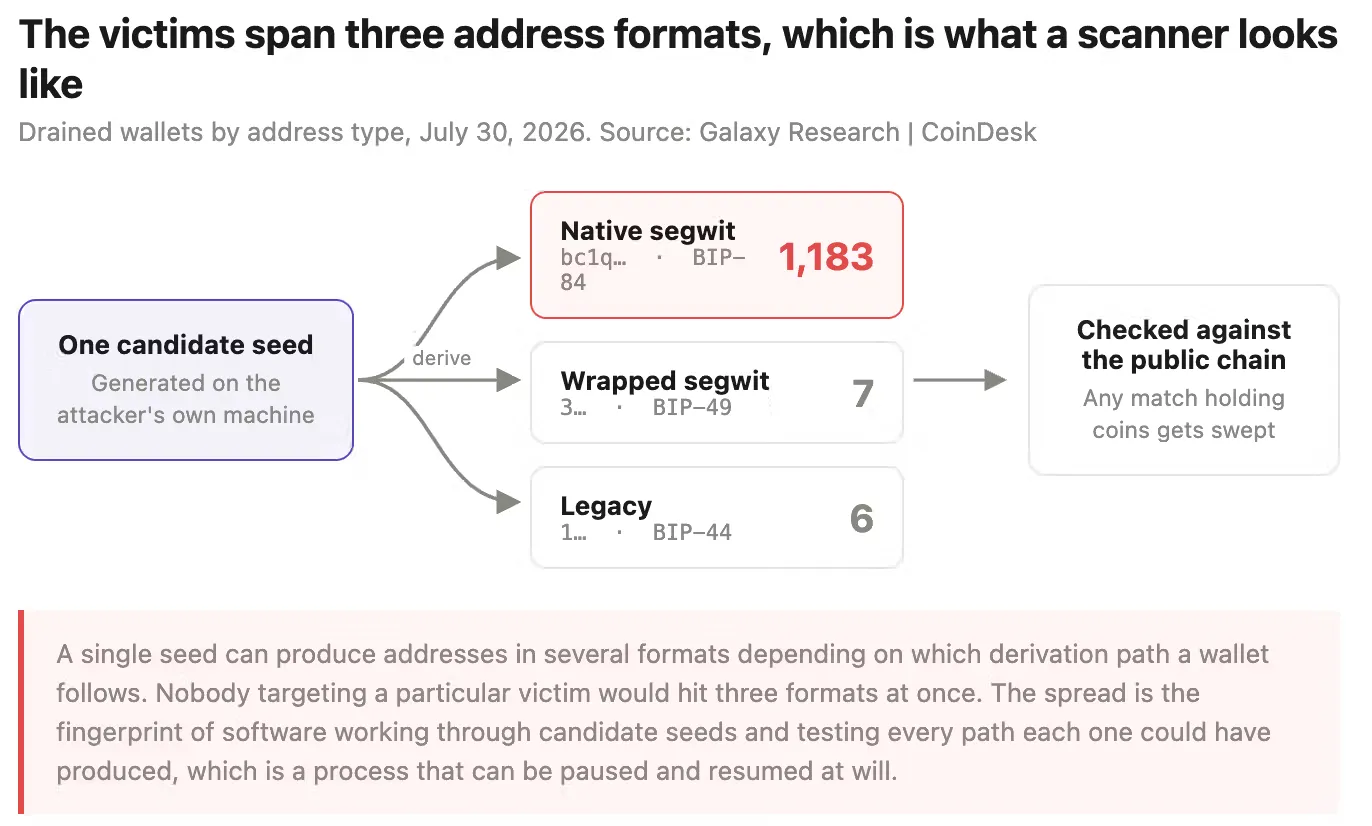
The victims span three address formats, which is what a scanner looks like. (Shaurya Malwa/CoinDesk)
Nor can an owner determine whether they are exposed. There is no test to run against your own wallet that reveals whether your seed sits inside the reproducible range.
Attack might not be fully finished
Coinkite, Coldcard's maker, has warned Mk3 owners and says its newer devices are unaffected, while Block's report places the Mk2, Mk4, Q and Mk5 in scope as well. Until that is resolved, anyone who generated a seed on the affected firmware has to assume the worst rather than verify it.
The attacker did make one mistake, however.
Block's Clay Garrett said on X that the operator used a paid account at a “well-known blockchain data provider” to query the source addresses during the sweeps, and that the provider's internal logs matched the suspected workflow with what he called extraordinary specificity, down to the number, timing and sequence of requests.