




The Iranian crypto exchanges wallets were exploited for at least $73 million as attackers used vanity addresses for the theft.
Update, June 18, 8:01 am UTC: This article has been updated to include a section on Gonjeshke Darande.
Iran-based cryptocurrency exchange Nobitex has been exploited for over $73 million of digital assets, according to onchain investigator ZachXBT.
The attack, disclosed in a Wednesday Telegram post, drained at least $73 million in assets across the Tron network and Ethereum Virtual Machine (EVM)-compatible blockchains, though only a portion is confirmed lost.
ZachXBT spotted attackers using a “vanity address” to exploit the protocol, which resulted in “suspicious outflows” from multiple Nobitex-linked wallets.
A vanity address refers to a public wallet address with a specific, user-defined sequence of characters. The first $49 million was stolen through the address “TKFuckiRGCTerroristsNoBiTEXy2r7mNX.” The second address used was “0xffFFfFFffFFffFfFffFFfFfFfFFFFfFfFFFFDead,” according to Tronscan.
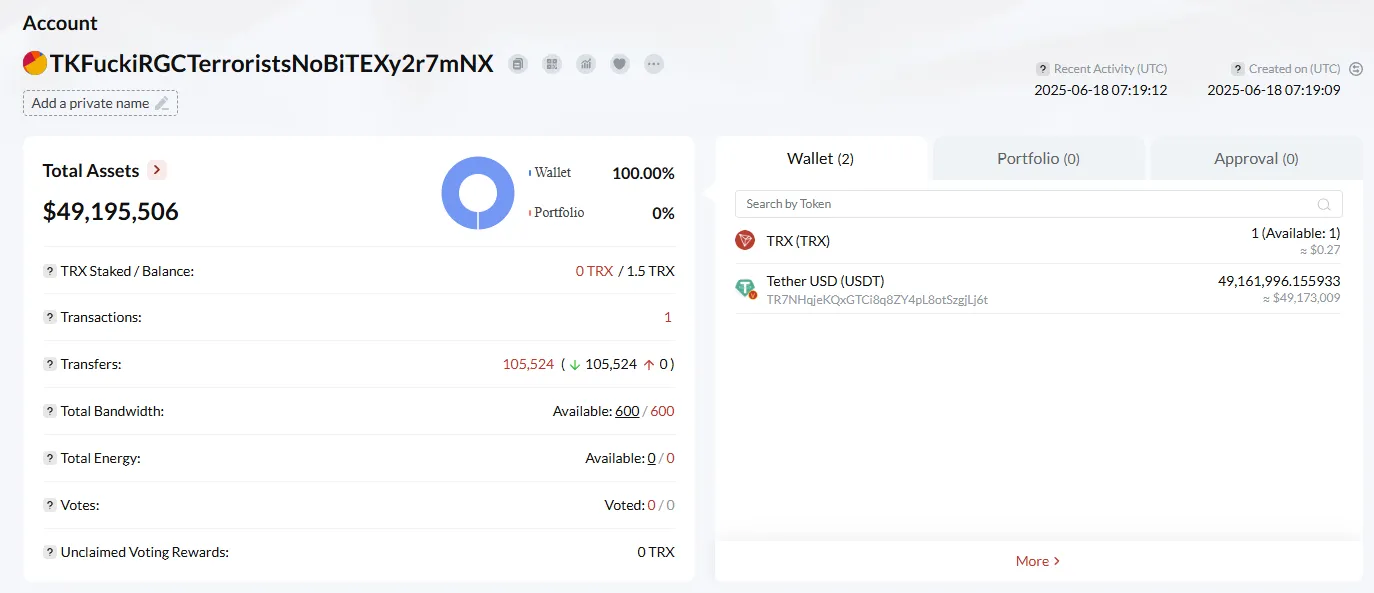
Attacker wallet “KFucki.” Source: Tronscan
Nobitex confirmed that a portion of its hot wallets saw signs of “unauthorized access” and was immediately “suspended” upon detection.
“Users assets are completely secure according to cold storage standards, and the above incident only affected a portion of the assets in hot wallets,” Nobitex said in an X post, adding that “all damages will be compensated through the insurance fund and Nobitex resources.”
The breach adds to a growing list of crypto industry hacks in 2025. More than $2.1 billion in digital assets have been stolen so far this year, according to blockchain security firm CertiK.
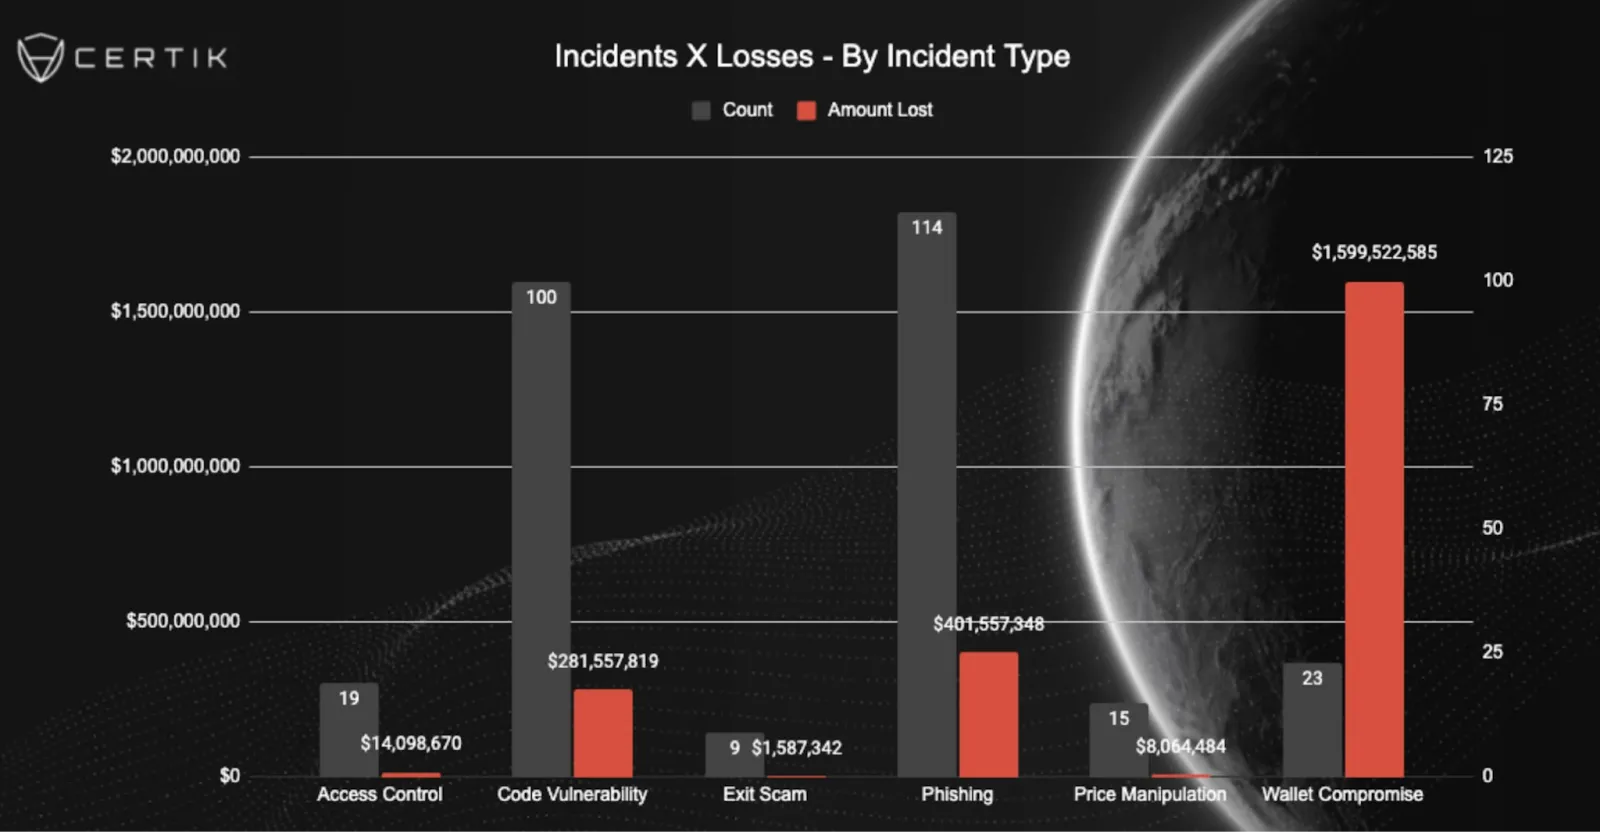
Source: CertiK
“The majority of this $2.1 billion was caused by wallet compromises, key mismanagement and operational issues,” Ronghui Gu, the co-founder of CertiK, told Cointelegraph during the Chain Reaction daily X spaces show on June 2.
He added that social engineering scams such as address poisoning are now more common than protocol-level hacks. These attacks rely on psychological manipulation to trick users into transferring assets to fraudulent wallets.
Pro-Israel hacker group claims responsibility
A pro-Israel hacker group calling itself “Gonjeshke Darande” has claimed responsibility for the Nobitex hack.
In a post on X, the group said it would release the exchanges source code and internal files within 24 hours, warning that any remaining assets on the platform “will be at risk.”
“The Nobitex exchange is at the heart of the regime‘s efforts to finance terror worldwide, as well as being the regime’s favorite sanctions violation tool,” the group wrote.
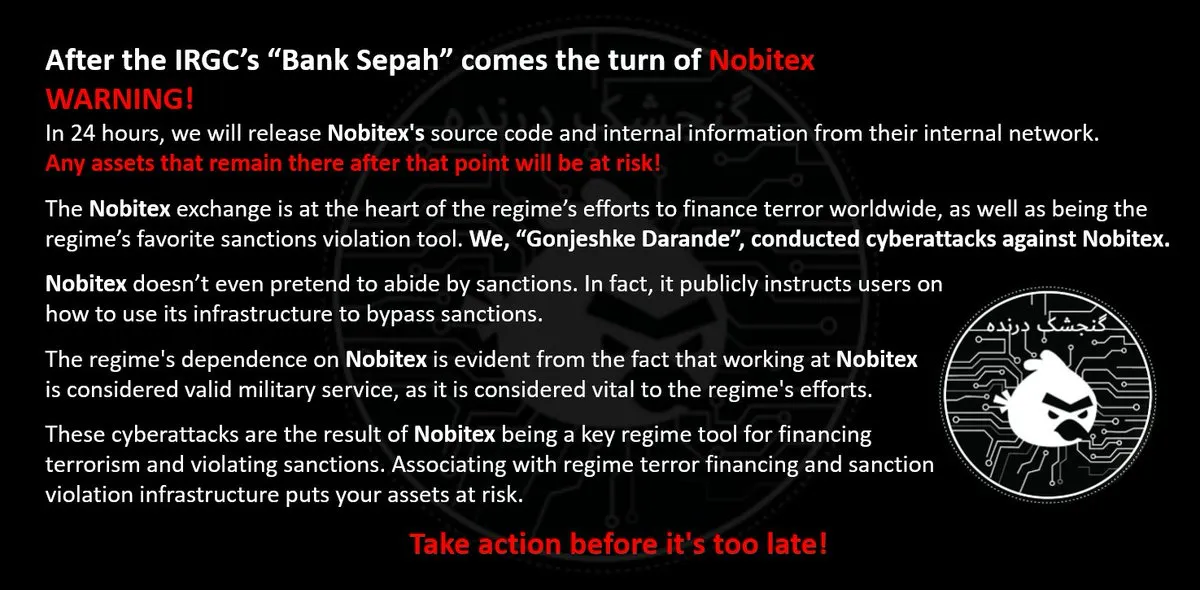
Sourc: Gonjeshke Darande
“The regime‘s dependence on Nobitex is evident from the fact that working at Nobitex is considered valid military service, as it is considered vital to the regime’s efforts,” the group said, urging users to “take action before its too late.”