




The hacker exploited a vulnerability in 1inchs Fusion v1 smart contract, which affected resolvers.
Update, March 8, 10:30 am UTC: This article has been updated to include new information confirming that the 1inch hacker returned most of the stolen funds after negotiations.
Decentralized exchange aggregator 1inch successfully recovered most of the $5 million stolen in a recent exploit after negotiating a bug bounty agreement with the attacker, the platform confirmed.
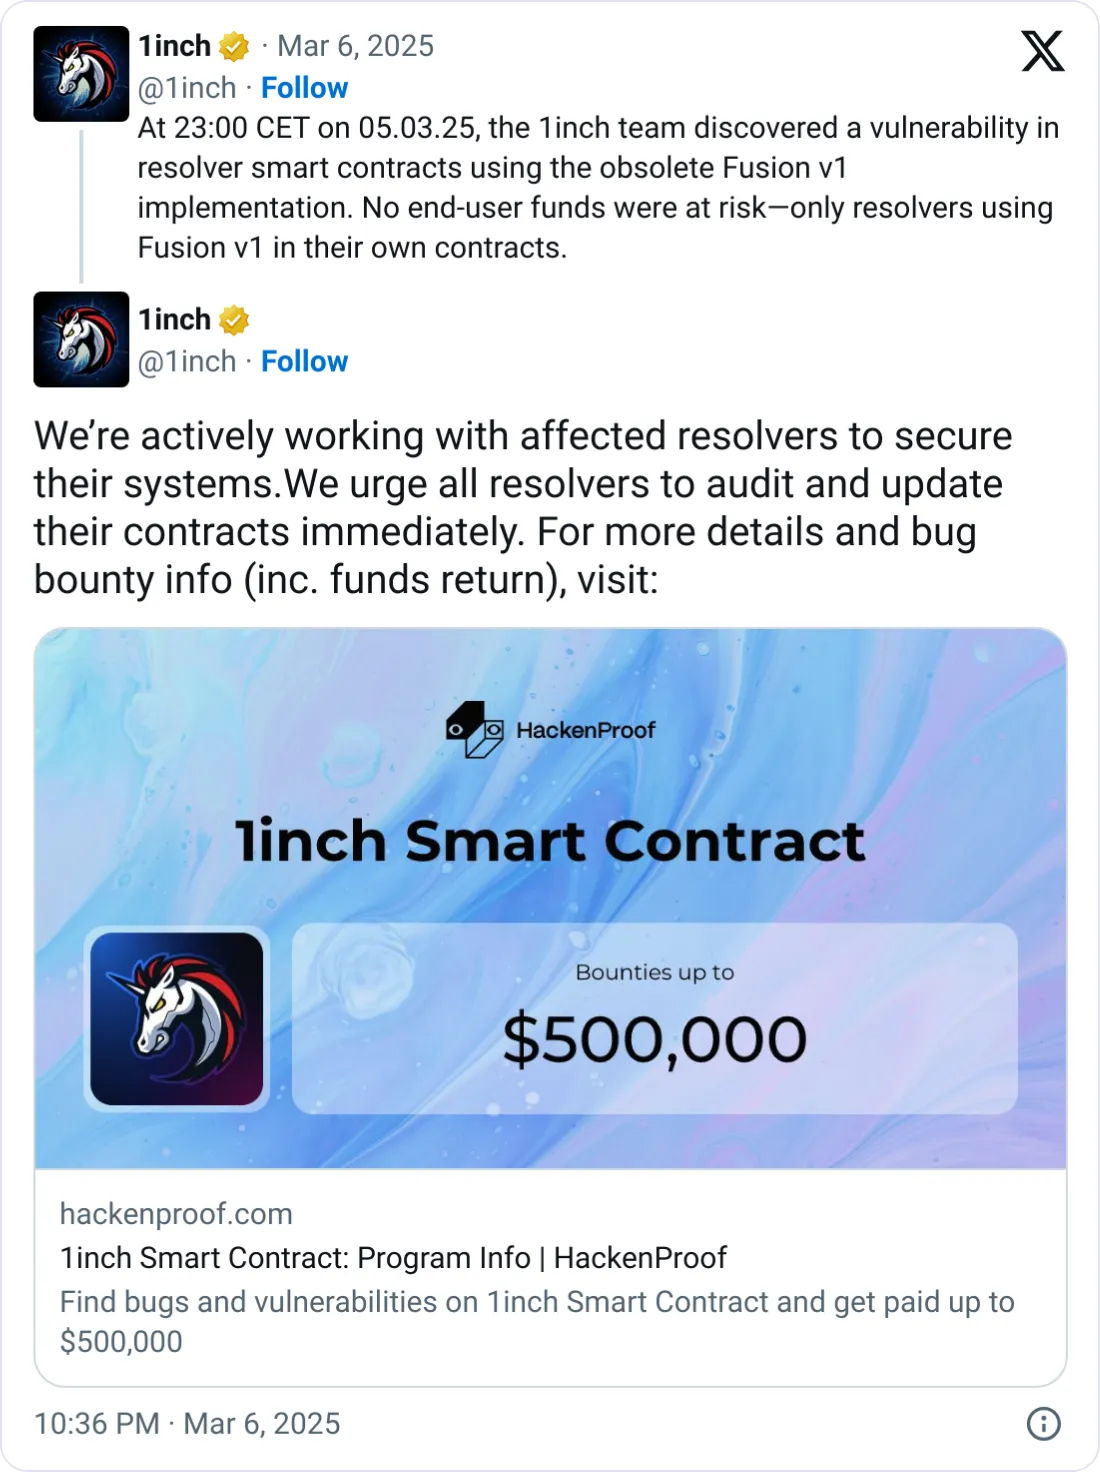
On March 5, 1inch identified a vulnerability affecting resolvers — independent entities that fill orders — using the outdated Fusion v1 implementation, which was made public a day later.
Source: 1inch Network
Tracing the $5 million 1inch hack
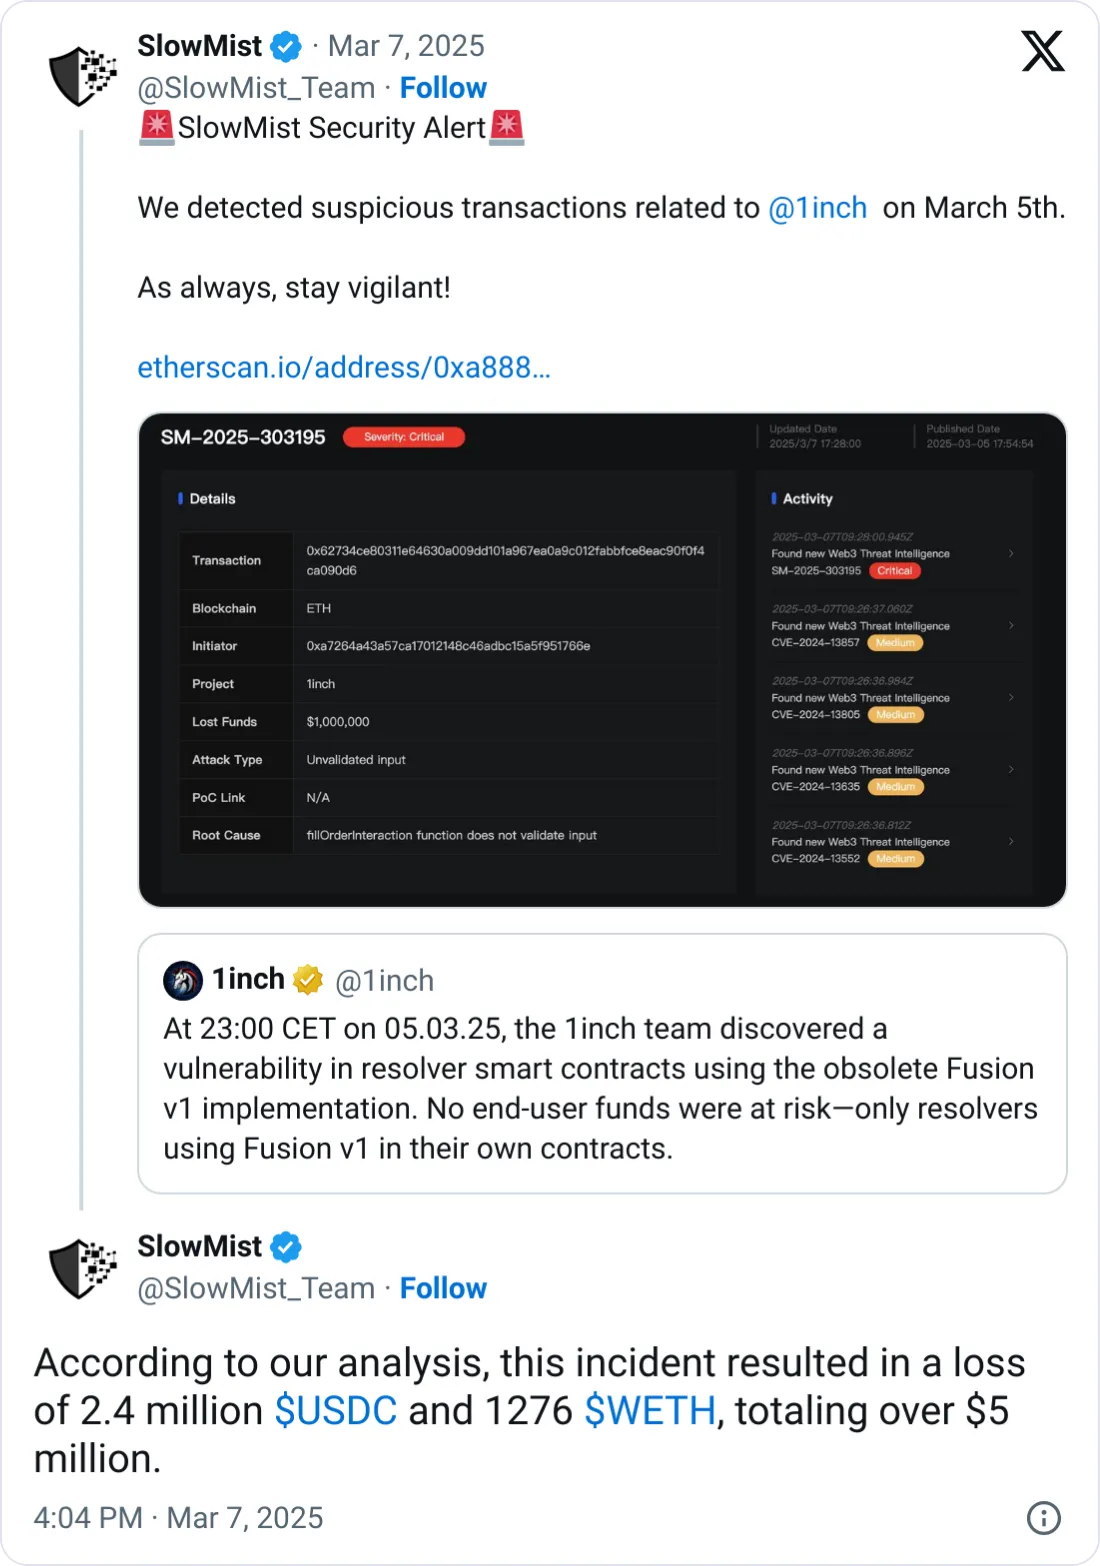
On March 7, blockchain security firm SlowMist found through an onchain investigation that the 1inch hacker made away with 2.4 million USDC (USDC) and 1,276 Wrapped Ether (WETH) tokens.
Source: SlowMist
According to 1inch, the hack stole funds only from resolvers using Fusion v1 in their own contracts, and end-user funds were safe:
“Were actively working with affected resolvers to secure their systems. We urge all resolvers to audit and update their contracts immediately.”Attacker agrees to return funds after negotiations
Following the exploit, 1inch and the affected resolver engaged in direct negotiations with the hacker to recover the stolen funds. Discussions centered on a bug bounty agreement, a practice where attackers return stolen assets in exchange for a portion of the funds as a reward for identifying vulnerabilities.
According to Decuritys postmortem report, the attacker agreed to return the majority of the stolen funds, keeping only the agreed-upon bounty amount. This approach has been increasingly used in crypto security incidents, as seen in past cases where hackers returned funds after negotiations.
1inch confirmed that the attacker returned the assets, effectively resolving the situation without further losses to the platform or its users.
Despite recovering the funds, 1inch emphasized the need for resolvers to update their contracts to prevent similar exploits in the future. The company stated:
“Were actively working with affected resolvers to secure their systems. We urge all resolvers to audit and update their contracts immediately.”
Bybit on the slow road to recovery
Recently, North Korean hackers behind the $1.5 billion Bybit hack — dubbed cryptos largest-ever heist — were successful in siphoning the entire amount despite coordinated efforts by the crypto community to recover the losses.
The hackers stole various amounts of liquid-staked Ether (STETH), Mantle Staked ETH (mETH) and other ERC-20 tokens from Bybit.
Despite the sudden loss of funds, Bybit managed to allow its users seamless withdrawal of their funds by quickly taking loans from other crypto companies, which were repaid at a later date.
It took 10 days for the Bybit hackers to launder $1.4 billion worth of stolen cryptocurrencies. Some of the laundered funds may still be traceable despite the asset swaps, according to Deddy Lavid, co-founder and CEO of blockchain security firm Cyvers:
“While laundering through mixers and crosschain swaps complicates recovery, cybersecurity firms leveraging onchain intelligence, AI-driven models, and collaboration with exchanges and regulators still have small opportunities to trace and potentially freeze assets.”
THORChain, a crosschain swap protocol, which was reportedly extensively used by the hackers to siphon funds, experienced a surge in activity post-Bybit hack.