




The $292 million KelpDAO bridge exploit in April and the Humanity Protocol private key theft in June were already suspected as connected, as both incidents carried hallmarks of DPRK-linked operations, with fingers pointing to the notorious Lazarus group.
Now, on-chain evidence shows the proceeds of those attacks are now flowing into shared wallets, which is a pattern consistent with a single laundering pipeline, according to blockchain analyst Specter.
How did the attackers move the Kelp DAO and Humanity protocol funds?
According to Specter, the Humanity Protocol attacker moved 15,403 $ETH, which is around $23.6 million, to a relatively new Ethereum address.
The funds were then crossed onto the Bitcoin network, where they mixed with proceeds that have been traced to the KelpDAO exploit.
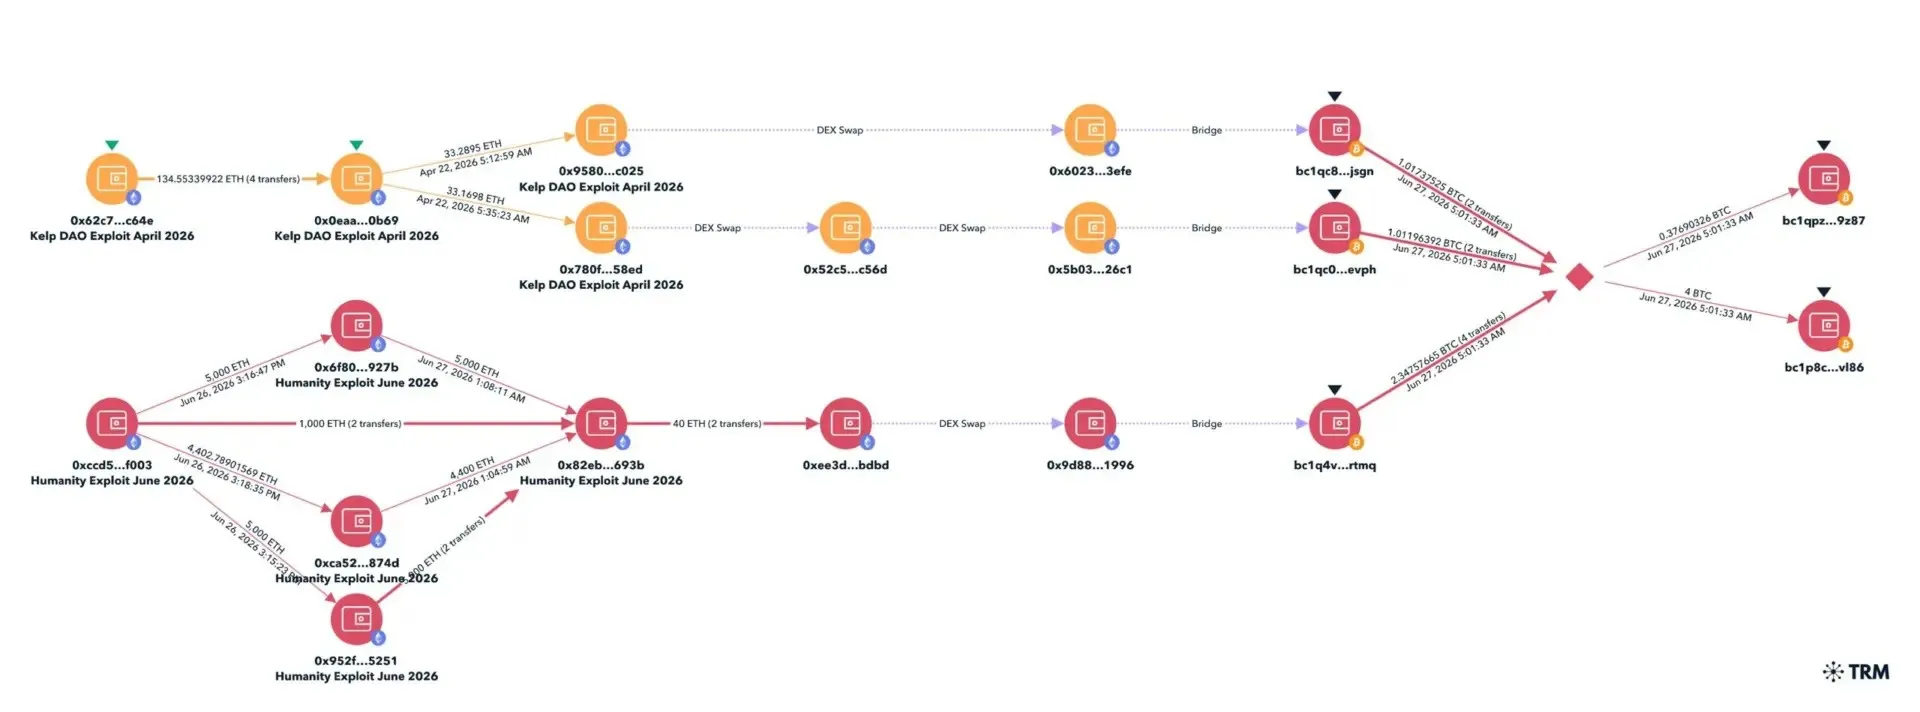
The funds stolen in the Humanity Protocol and KelpDAO attacks have landed in the same wallets, per ZachXBT and Specter. Source: TRM Labs
This action is a well-documented Lazarus Group technique, where they consolidate proceeds from separate operations into unified Bitcoin wallets before routing them through mixers and over-the-counter desks.
What connects the two exploits?
According to Chainalysiss investigation, the attackers behind the KelpDAO exploit on April 18 compromised internal RPC nodes operated by LayerZero Labs and launched a DDoS attack against external nodes simultaneously.
The attackers tricked the Ethereum bridge contract into releasing 116,500 rsETH without a corresponding token burn on the source chain.
The attack was attributed to the Lazarus Group. The Arbitrum Security Council froze over 30,000 $ETH of the attacker‘s downstream funds, and KelpDAO’s emergency pause also prevented another $95 million from being drained.
Although the Humanity Protocol breach did not follow the same pattern as the Kelp DAO attack, post-mortem reports now show that North Korea-linked bad actors were involved.
A Quantstamp incident report, prepared for Humanity Protocol on June 11, found that the attacker phished a company director, Chong Yee Wai, with a malicious email impersonating the Korean exchange Bithumb.
Quantstamp stated that the attack was “characteristic of DPRK intrusions.”
The malware gave the attacker remote desktop access to Chongs Windows machine. From there, the attacker copied MetaMask wallet keys and used them to mint and sell unauthorized $H tokens on both Ethereum and BNB Smart Chain. This caused the token to crash by roughly 89%.
Proceeds at known attacker addresses are worth over $21 million in $ETH, according to Quantstamps findings.
Legal complications add a twist to recovery efforts
Currently, plaintiffs hold over $877 million in unpaid U.S. court judgments against North Korea. In May, they served the Arbitrum DAO with a restraining notice on April 30, seeking to seize approximately 30,766 $ETH (about $71 million) of frozen funds.
The plaintiff claimed that since the funds were linked to North Korea, they had the right to seize any funds from groups linked to the country as part of the money owed in unpaid judgments.
Arbitrum already had a governance proposal in motion to transfer the frozen funds to a recovery initiative backed by Aave Labs, KelpDAO, LayerZero, EtherFi, and Compound, which would compensate affected users.
A court later approved the Arbitrum vote to move the Kelp funds back to Aave. How the plaintiff reacts to this newfound confirmation of North Koreas involvement is yet to be seen, but going by past incidents, chances are high that the Humanity Protocol loss and possible recovery could also come under litigation.