




Two members of the Balancer protocol community submitted a proposal on Thursday outlining a distribution plan for a portion of the funds recovered from the protocols $116 million November exploit.
About $28 million from the $116 million heist was recovered by white hat hackers, internal rescuers, and StakeWise — an Ether liquid staking platform.
However, the proposal covers only the $8 million recovered by white hat hackers and internal rescue teams, while the nearly $20 million retrieved by StakeWise will be distributed separately to its users.
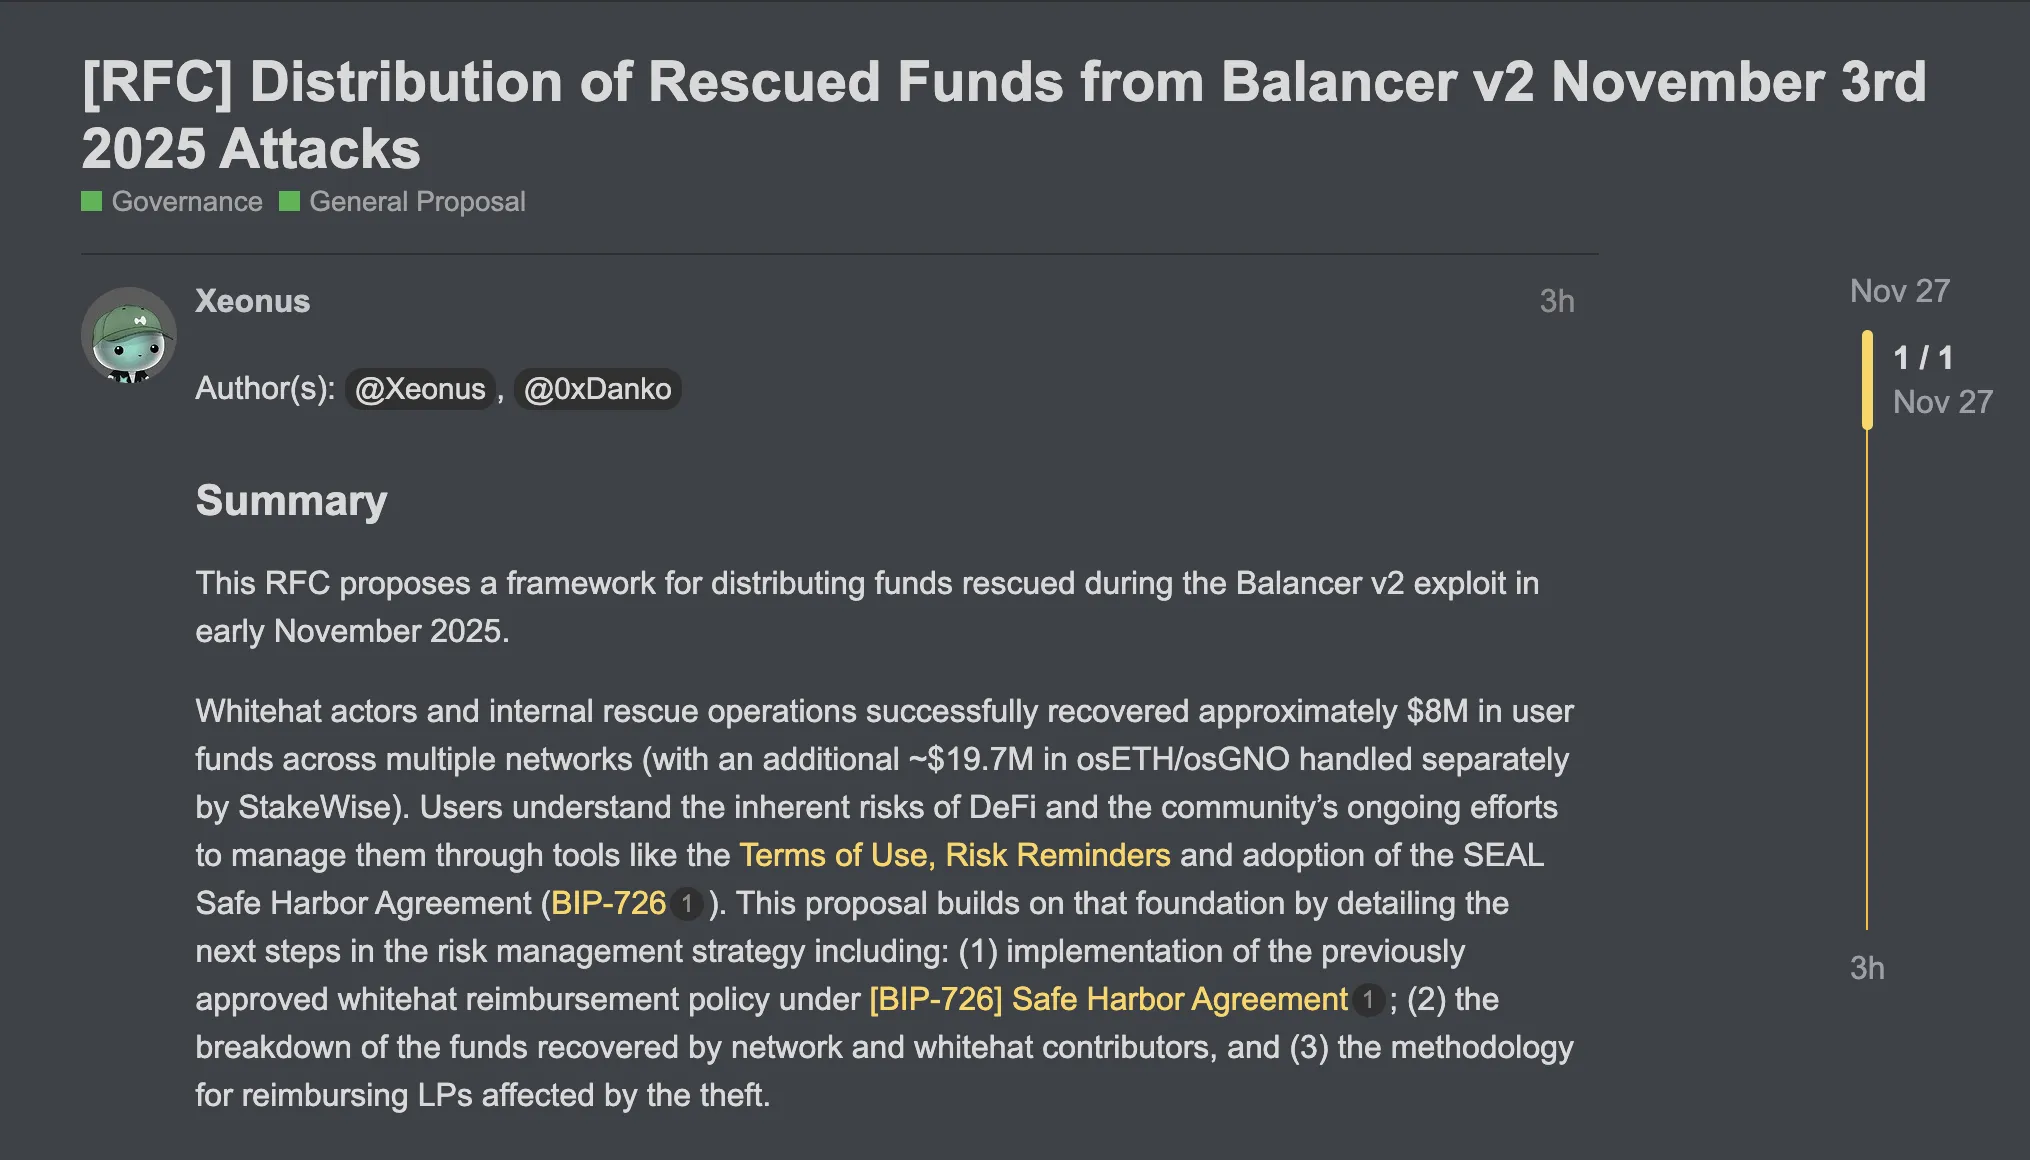
Balancer community proposal to distribute recovered funds. Source: Balancer
The authors proposed that all reimbursements should be non-socialized, meaning that funds are distributed only to the specific liquidity pools that lost the funds and paid out on a pro-rata basis according to each holders share in the liquidity pool, represented by Balancer Pool Tokens (BPT).
Reimbursements should also be paid in-kind, with victims of the hack receiving payment denominated in the tokens they lost to avoid price mismatches between different digital assets, according to the authors.
The Balancer hack was one of the “most sophisticated” attacks in 2025, according to Deddy Lavid, the CEO of blockchain cybersecurity company Cyvers, highlighting the need for crypto user safety as security threats continue to evolve.
Related: Balancer makes last appeal to hacker behind $100M+ exploit
Top blockchain security firms audited Balancer‘s smart contracts, but the audits didn’t save it
Balancer‘s code has been audited 11 times by four different blockchain security companies, according to the platform’s GitHub page.
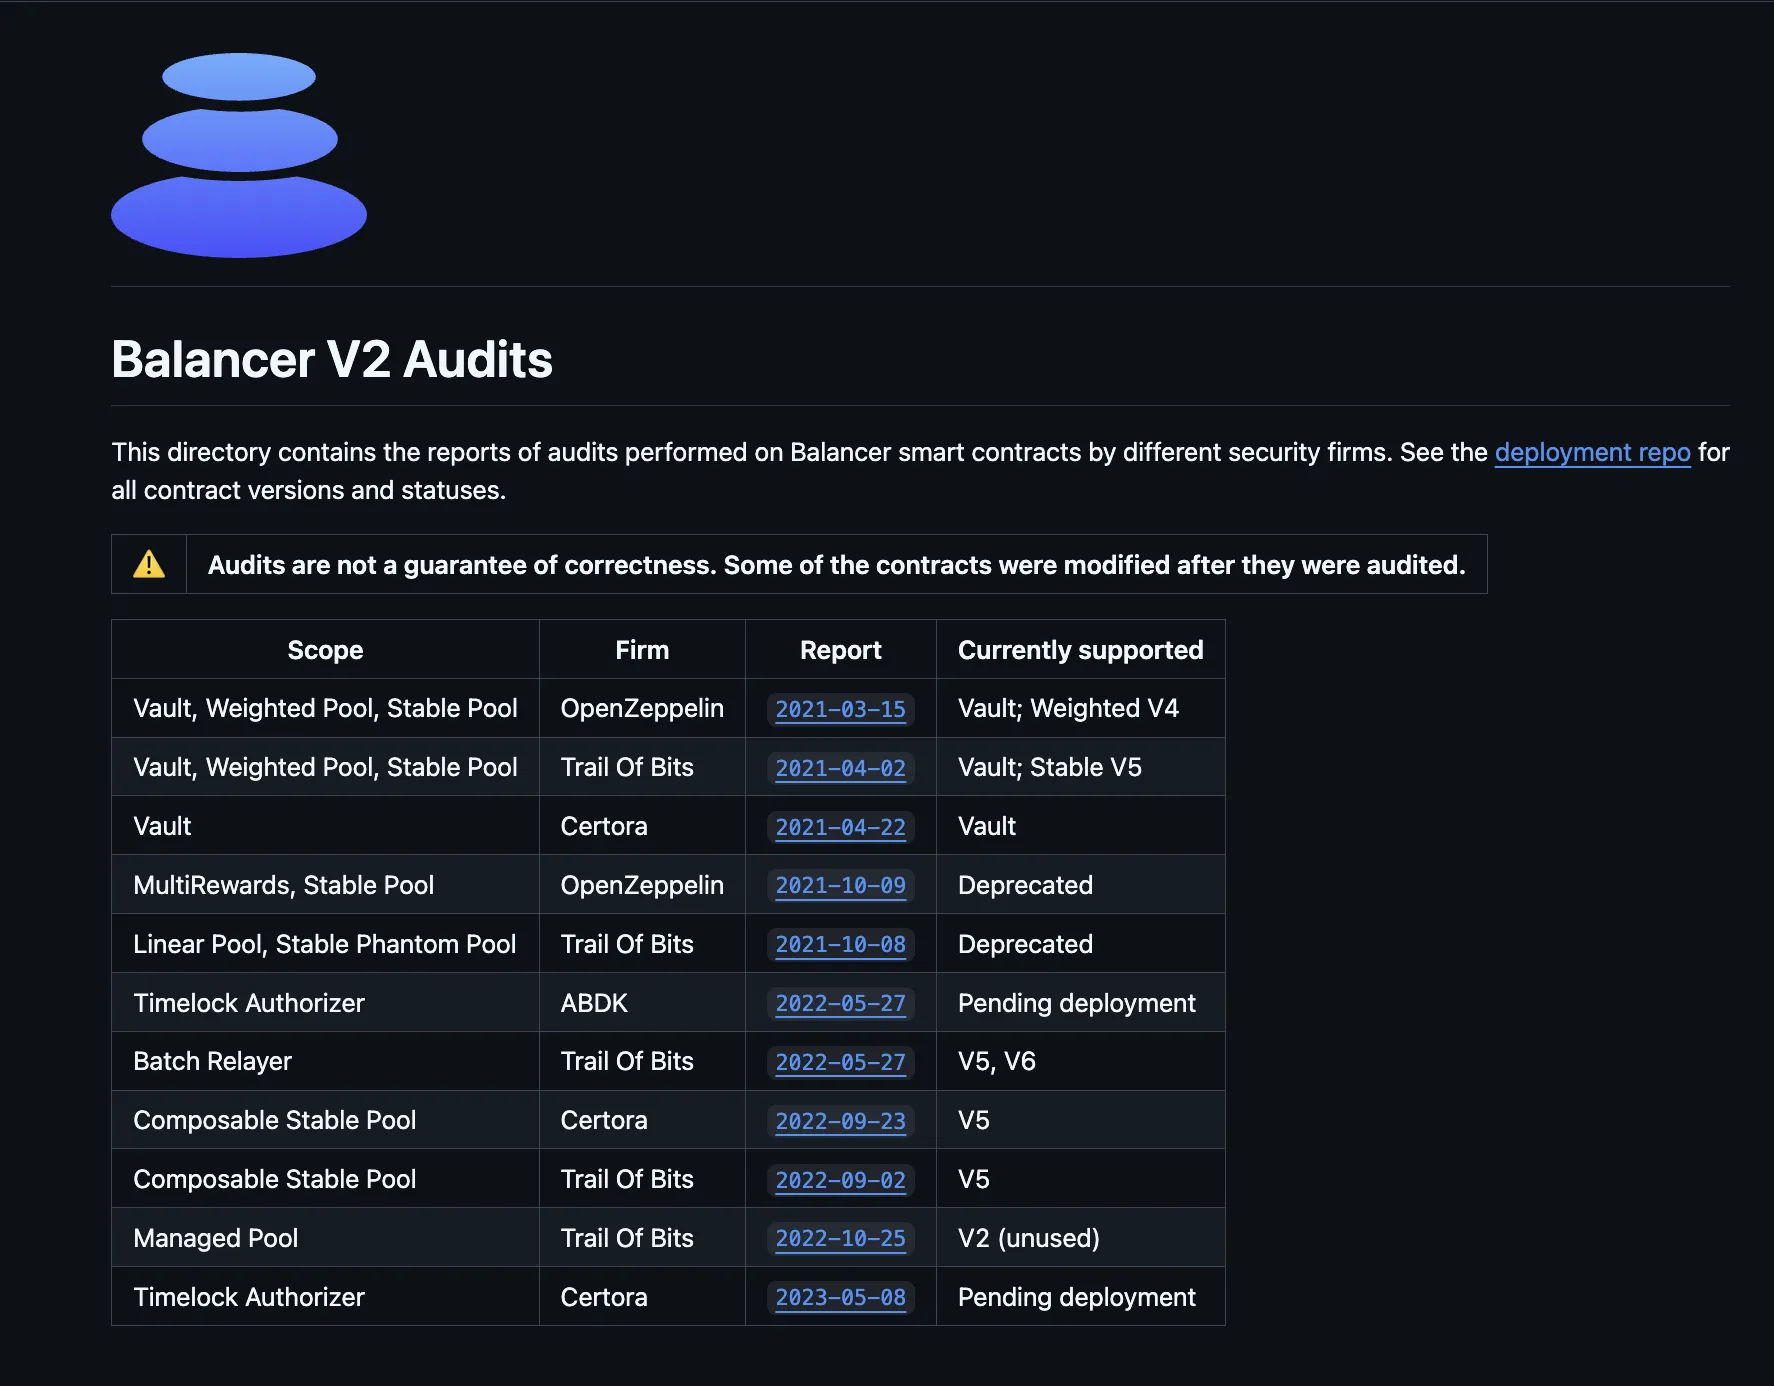
Balancer code audits. Source: GitHub
Despite the audit, the platform was still hacked, prompting some crypto users to question the value of audits and whether they actually ensure code safety.
Balancer released a post-mortem report on Nov. 5 outlining the root cause of the hack: a sophisticated exploit targeting a rounding function used in EXACT_OUT swaps within its Stable Pools.
The rounding function is designed to round down when token prices are input, but the attacker managed to manipulate the calculation so that values were rounded up instead.
The attacker combined this flaw with a batched swap — a single transaction containing multiple actions — to drain funds from Balancers pools.