




Decentralized finance protocol Echo Protocol was exploited after an attacker minted about 1,000 unauthorized eBTC on the protocol, which is deployed on the Monad blockchain.
Blockchain security firm PeckShield and analytics platform Lookonchain both reported the incident on Tuesday, noting that a hacker minted 1,000 synthetic Bitcoin (eBTC) worth around $76.7 million.
“We are currently investigating a security incident impacting the Echo bridge on Monad. All cross-chain transactions remain suspended while the investigation is underway,” Echo Protocol said on Tuesday.
This latest exploit comes in a month that has seen at least 12 protocols compromised, including THORChain, Verus Protocols Ethereum bridge, Transit Finance, TrustedVolumes and Ekubo.
According to PeckShield, the attacker attempted to launder some of the loot by depositing 45 eBTC worth around $3.45 million into DeFi lending and liquidity management protocol Curvance.
The attacker then borrowed 11.3 wrapped Bitcoin (wBTC) worth $868,000 against it, bridged the tokens to Ethereum, swapped them for $ETH, and sent 384 $ETH worth about $822,000 to the Tornado Cash mixing service.
The attacker still holds 955 eBTC worth about $73 million, according to DeBank.
Echo Protocol is a Bitcoin DeFi platform focused on Bitcoin liquidity aggregation, liquid staking, restaking, and yield generation. It creates unified, liquid BTC assets such as eBTC for users to bridge and deploy in DeFi for additional yield. The protocol is deployed on Monad, a high-performance, layer-1, EVM-compatible blockchain.
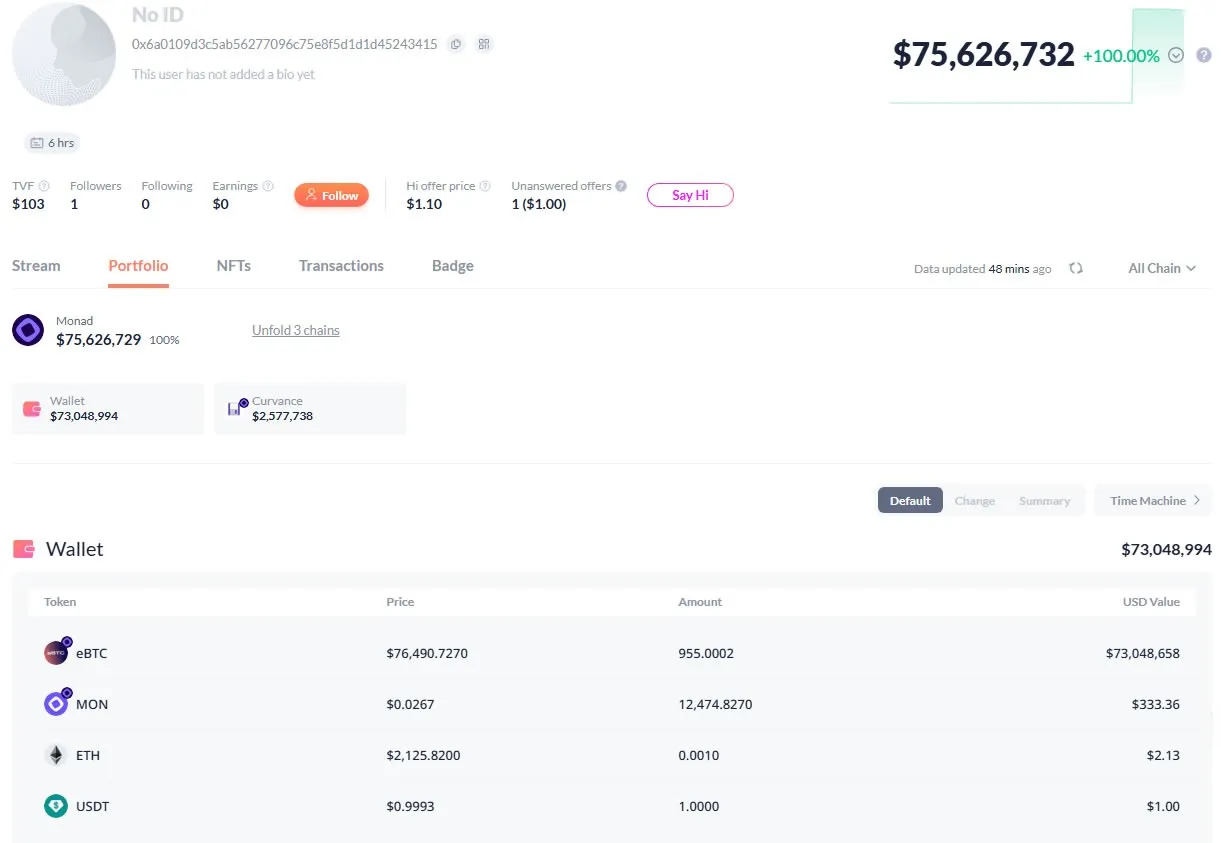
The hacker still holds 95% of the stolen crypto. Source: DeBank
Admin private key compromised
Blockchain developer “Marioo” reported that it was not a smart contract bug, but an admin private key compromise, and the root cause was “operational, not technical.”
The eBTC contract “worked exactly as designed,” they said, adding that the vulnerabilities included a single signature for the admin role, no timelock, no minting supply cap or rate limit, and no “supply sanity check” by Curvance for the freshly minted collateral.
Related: Hackers used AI to craft zero-day attack to bypass 2FA: Google
Curvance reported that it was aware of the “anomaly” detected in the Echo eBTC market on Curvance and confirmed that there was no compromise with its own smart contracts. It paused the affected market for investigation.
Monad co-founder Keone Hon clarified on X that “the Monad network is not affected and is operating normally.”
Meanwhile, Echo Protocol said it will provide updates through its official channels as more information becomes available.
DeFi hacks surge in 2026
The year has been challenging for DeFi security, with dozens of protocols exploited for hundreds of millions in crypto and more than 20 protocols shuttering services.
Two of the largest hacks this year included the exploit of the Drift Protocol, which lost $285 million, and Kelp DAO, which was exploited for $292 million in April.
On Monday, Verus Protocols Ethereum bridge was exploited through a fake cross-chain transfer message that allowed a hacker to steal at least $11.6 million in crypto.
Decentralized liquidity protocol THORChain halted trading on Friday after blockchain investigator ZachXBT flagged a suspected $10 million exploit.
Meanwhile, Transit Finance suffered a deprecated smart contract exploit, resulting in the loss of $1.88 million last week.