




The US Department of Justice said Thursday it had obtained court authorization to seize or restrain more than $1.2 billion of the $6.3 billion in cryptocurrency stolen from Binance.
The authorization covers part of the more than $2.7 billion in stolen assets that US authorities and private-sector partners have frozen since the Oct. 29 hack. Investigators are still working to recover additional funds, the department said in its announcement.
The FBI attributed the Binance hack to North Korea‘s TraderTraitor group in a cyber alert. Kim Yo Jong, the sister of North Korean leader Kim Jong Un, denied North Korea’s involvement.
Binance said it had covered the affected assets with its own funds and that a new proof-of-reserves snapshot showed at least one-to-one backing for customer assets, according to its Thursday post on X.
In November 2025, the DOJ announced a separate enforcement action targeting about $15 million in cryptocurrency linked to North Korean hackers known as APT38.
Related: Crypto hack losses equal 57 cents per $1 earned onchain: Arks Valente
FBI warns of FaceStealers deepfake video calls
In a separate case, US authorities seized cloud infrastructure used in FaceStealer, a North Korean social engineering campaign that stole more than $400 million in cryptocurrency over the past 18 months, the DOJ said.
The hackers used secretly recorded footage of previous victims and AI-generated deepfakes of prominent crypto figures to gain targets trust on video calls. They used bogus technical fixes to trick targets into installing malware, the DOJ said.
The campaign targeted people working in crypto and Web3. The hackers also increasingly targeted open-source software developers and maintainers in attempts to gain access to their devices and software repository accounts.
The FBI seized more than 900 webcam videos of FaceStealer victims under a federal warrant. The bureau also published guidance on how to protect against the scheme and what to do after a compromise in a public advisory.
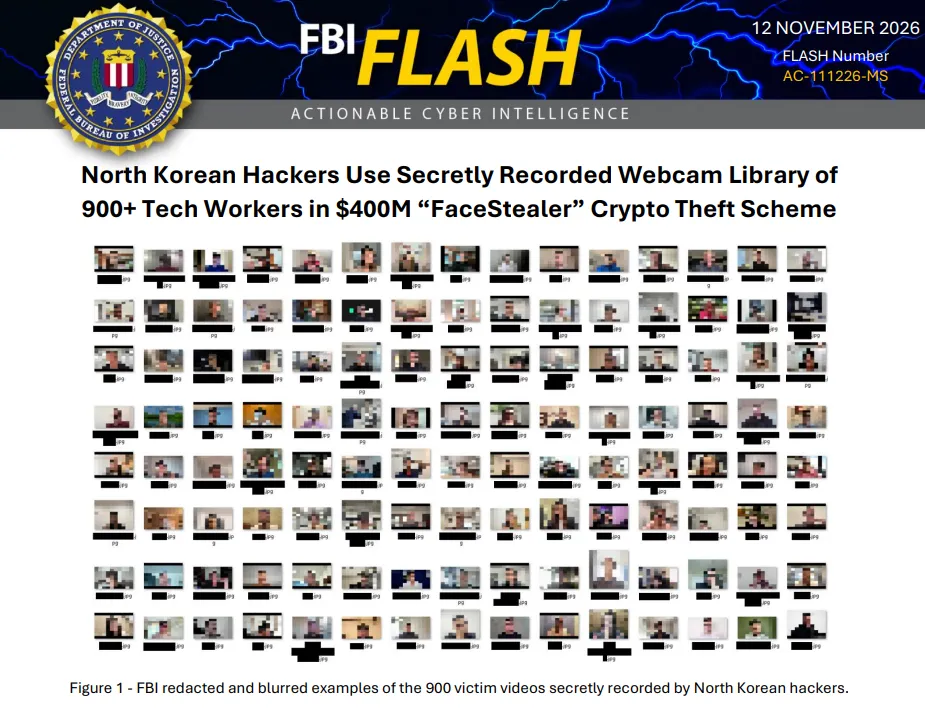
Redacted stills from webcam videos recorded by FaceStealer hackers. Source: FBI
The DOJ said the hackers behind FaceStealer are known publicly by several names, including Sapphire Sleet, UNC1069, Dangerous Password, CryptoCore, APT38, BlueNoroff and Stardust Chollima.