






Binance founder Changpeng Zhao says AI doesn‘t need to break Bitcoin’s cryptography to cause damage. Instead, he warns that leaked data already fuels phishing and social engineering.
Meanwhile, Bitcoin Core developers are changing how they disclose bugs as AI makes flaws easier to find.
Sponsored
Sponsored
Why CZ Sees Phishing as the Bigger AI Threat
Zhao, known as CZ, made the point in an X post on October 23. He argued that cryptos encryption is not the weak link.
In fact, he said banks and much of the internet rely on weaker encryption than Bitcoin. As a result, those legacy systems would face greater risk if AI code-breaking became a serious threat.
However, AI can already make scams more convincing. Attackers combine old leaked personal data with polished, AI-written messages that seem to come from real contacts. CZ closed his post with a familiar reminder: “Stay SAFU!”
CZ‘s view contrasts with a warning from Ethereum researcher Justin Drake on October 8. Drake urged the industry to “calmly start planning for ’bunker mode.” In a worst case, he said, AI could break the math protecting wallets “in months, not years.”
Still, no practical attack has emerged so far. Drake suggested that large holders gradually move funds to addresses whose public keys have never appeared on-chain.
Sponsored
Sponsored
How Is Bitcoin Core Responding to AI-Discovered Bugs?
Bitcoin Core developer Antoine Poinsot announced a new security policy on the Bitcoin Development Mailing List on Thursday. He said large language models now make some flaws easy to rediscover.
As a result, Poinsot said long embargoes on those bugs achieve little. They also delay fixed releases for users.
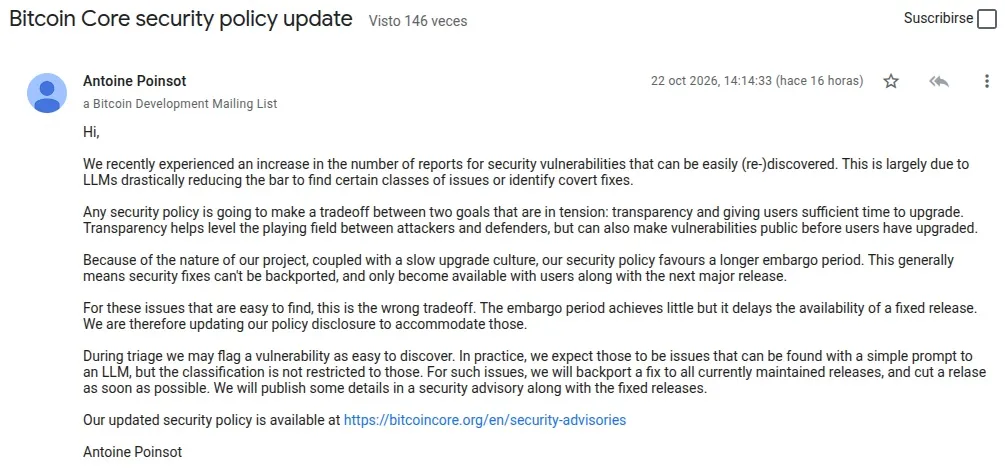
Bitcoin Core Security Policy Update. Source: Google Groups
Under the new rules, easily discoverable vulnerabilities will receive fixes as soon as possible across all maintained versions. Security advisories will accompany those updates.
Other bugs follow severity-based timelines. Low-severity issues become public two weeks after a major release includes the fix. Meanwhile, medium- and high-severity flaws stay private until the last affected version reaches end of life. Critical bugs, however, will likely need a separate process.
Together, both developments show how quickly AI is reshaping crypto security, from user scams to core software.